 Digital Cookie News



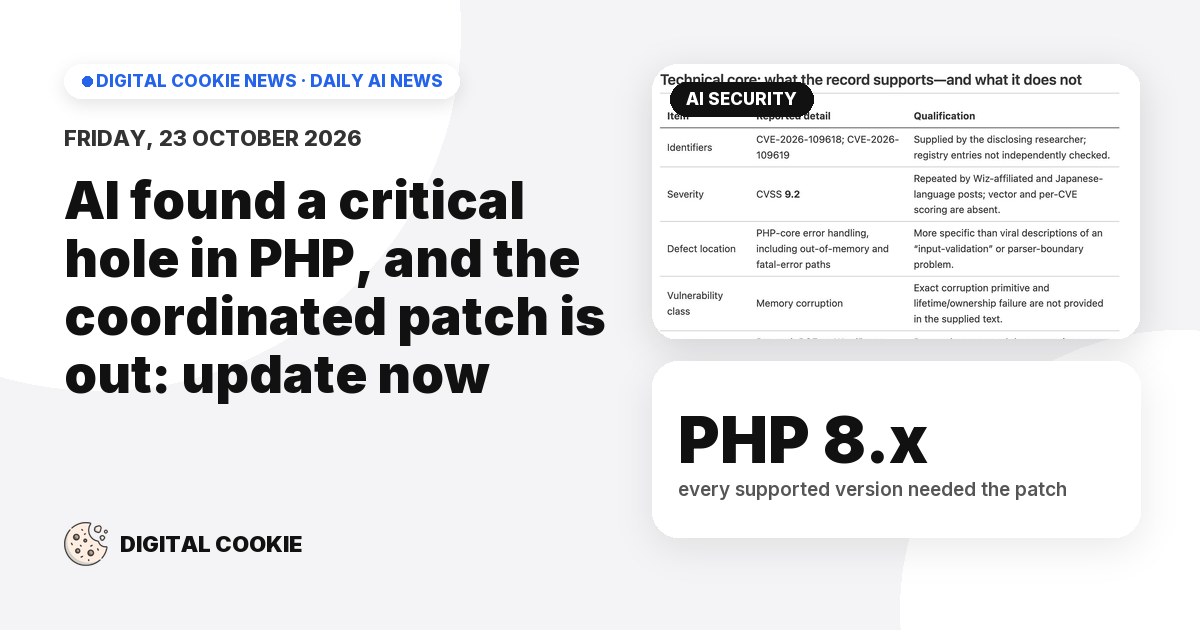
PHP 8.xevery supported version needed the patch
Two memory-corruption bugs in the PHP engine, nicknamed PHP2Shell, were found separately by a researcher using OpenAI's Patch the Planet program and by Wiz Research using frontier models. Researchers showed remote code execution on WordPress, Drupal and Joomla before login. After about two months of coordination, patched PHP 8.x releases shipped on Oct 21, a day early because the CVE IDs leaked.
Key points
- The patches cover the whole PHP 8.x line; Cloudflare shipped stopgap firewall rules for every plan while sites update.
- The release was pulled forward after the CVE IDs leaked with a wrong severity score (10.0 instead of 9.2), and a mistakenly published proof-of-concept video sped up exploit work.
- OpenAI published a Codex Skill A saved, reusable set of instructions (and sometimes code) that an AI agent loads when a task needs it. that walks site owners through checking exposure, a helper rather than a substitute for vendor advisories.
- Credit is disputed, and viral outage claims are uncorroborated: "All high profile cyber disclosures are at least a little bit of marketing."
Why it matters: Any client site on WordPress, Drupal or Joomla should be patched now, and asking a coding agent to scan your own projects for affected dependencies is a quick first check.